Table of Contents
- Understanding Modern Web Security
- The Architecture of Secure Auth
- Choosing the Right Authentication Strategy
- Next.js Authentication Best Practices
- Handling Sessions and Tokens
- Server-Side vs Client-Side Security
- Protecting API Routes
- Middleware for Access Control
- Database and Data Storage Security
- Common Pitfalls to Avoid
- Performance Considerations for Auth
- Scalability in Auth Systems
- Integration with Third-Party Providers
- Conclusion
Understanding Modern Web Security
Building a robust application today requires more than just a password field and a database. Security is the foundation of every high-quality application, especially when dealing with user data and private resources.
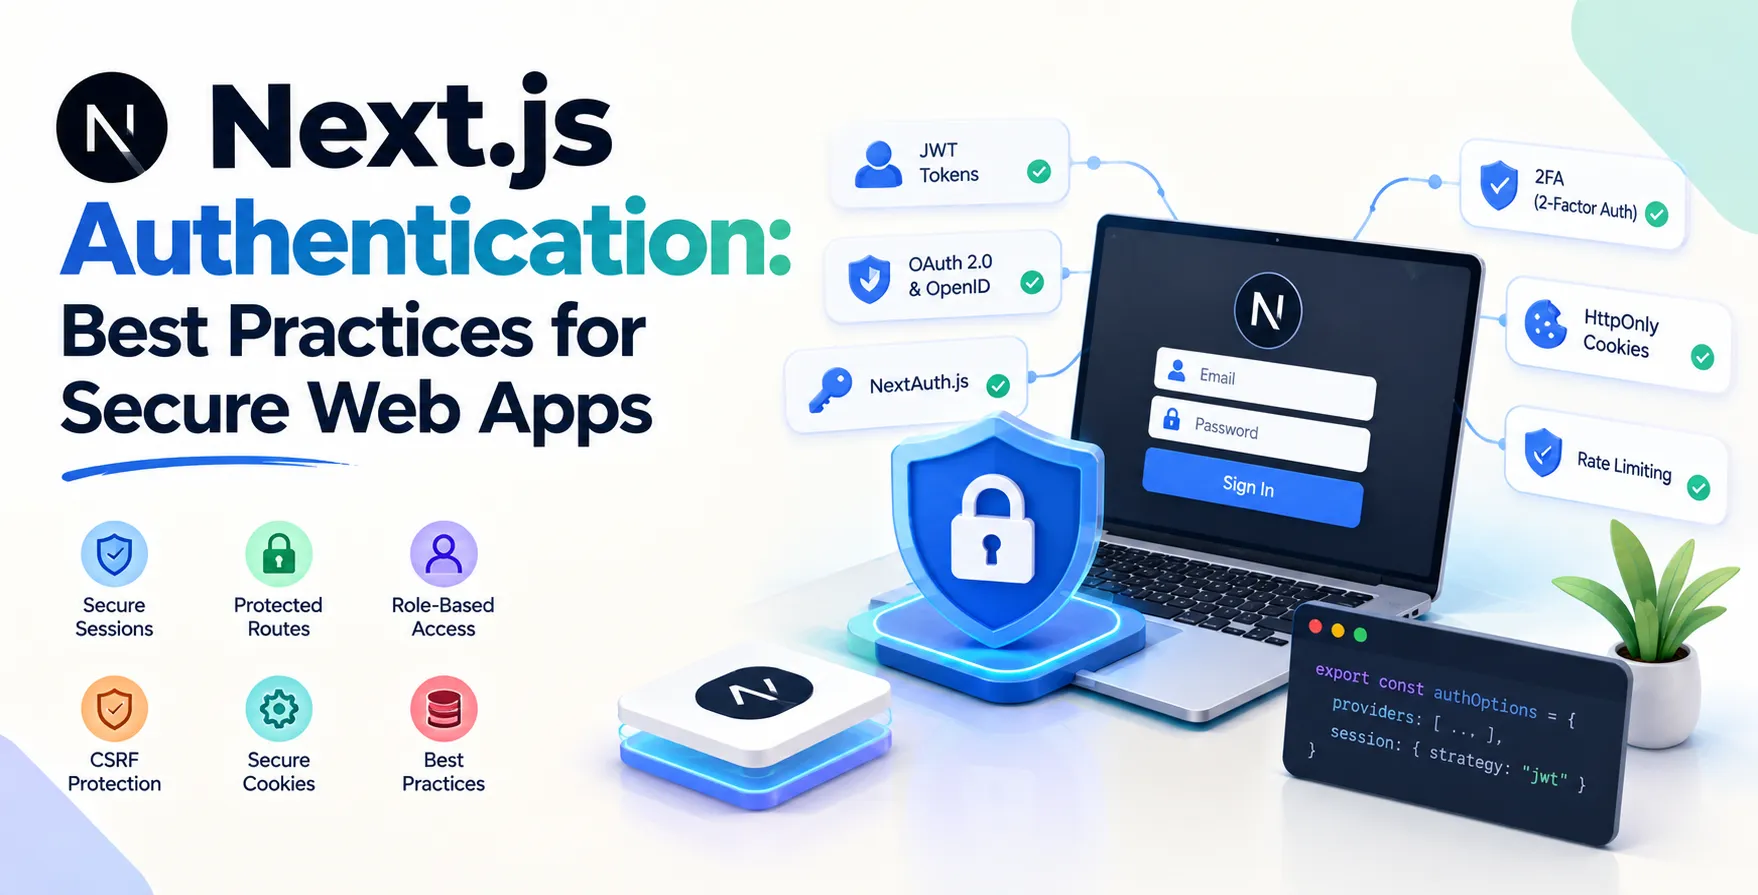
Developers must adopt a defense-in-depth mindset to ensure that no single point of failure compromises the entire system. Implementing Next.js authentication requires careful planning and a deep understanding of how modern browsers and servers communicate sensitive information.
- Prevents unauthorized data access
- Ensures compliance with privacy regulations
- Builds trust with end users
The Architecture of Secure Auth
Authentication in a modern framework is fundamentally different from traditional monolithic patterns. You are no longer just managing a session cookie on a single server; you are likely orchestrating token exchanges across distributed environments.
A well-architected system separates authentication logic from the UI. This allows for better maintainability when your application grows beyond simple form submissions into complex SaaS development scenarios.
- Decouples identity from business logic
- Simplifies cross-platform integration
- Supports stateless authentication flows
Choosing the Right Authentication Strategy
Selecting the right method for your project is the first step in successful Next.js auth implementation. The choice often depends on whether you are building a simple portal or a complex platform requiring enterprise-grade identity management.
OAuth and OpenID Connect
These protocols are industry standards for modern web applications. They allow users to log in securely without you ever touching their actual passwords.
- Supports social login integrations
- Reduces risk of credential leakage
- Standardizes identity verification
JSON Web Tokens
JWTs are excellent for stateless communication between your frontend and your backend. They contain all the necessary information in a signed package, making them highly efficient for custom software development projects that use microservices.
- Stateless session management
- Easily verified across multiple services
- Reduces database lookup overhead
Next.js Authentication Best Practices
Security is not a feature you add at the end of a project. It must be ingrained in your development lifecycle from the first commit to ensure secure Next.js authentication is maintained throughout the application's lifespan.
Always favor established libraries over rolling your own security logic. Libraries like Auth.js have been battle-tested by the community to handle edge cases that are easy to miss.
- Use battle-tested libraries
- Enforce strict environment variable management
- Regularly rotate signing secrets
- Implement rate limiting on login routes
- Audit dependencies for vulnerabilities
Handling Sessions and Tokens
Managing sessions securely is critical in a server-rendered environment. You need to ensure that tokens are not accessible to malicious scripts through Cross-Site Scripting (XSS) attacks.
Always store your session identifiers in HttpOnly, Secure cookies. This prevents JavaScript from reading the cookie, significantly lowering the risk of session hijacking in your web development projects.
- Use HttpOnly cookie flags
- Set strict SameSite attributes
- Implement automatic token refreshing
Server-Side vs Client-Side Security
Never trust the client to perform security checks. While you might hide a button on the UI, that does not stop a malicious user from hitting your API directly if you haven't secured the server-side logic.
Your server is the only source of truth. Always validate identity on every request before returning sensitive data from your database or external APIs.
| Security Aspect |
Client-Side |
Server-Side |
| Session Validation |
Risky |
Required |
| API Access |
Not allowed |
Verified |
| Role Checks |
UI display only |
Enforced |
| Data Filtering |
None |
Primary |
| Sensitive Logic |
None |
Exclusively |
Protecting API Routes
Next.js API routes act as the bridge between your client and your data. If these are not secured, your database is effectively open to the public internet.
When designing these routes, treat every request as an unauthenticated one until proven otherwise. Validate the session or token headers strictly before proceeding with any database operations.
- Validate tokens on every request
- Return 401 for missing credentials
- Return 403 for insufficient permissions
Middleware for Access Control
Next.js middleware is a powerful tool for intercepting requests before they reach your pages or API routes. It allows you to enforce authentication rules globally or on specific paths without duplicating logic across your codebase.
Use middleware to check for the presence of a session cookie or a valid JWT. If the user is not authenticated, you can immediately redirect them to the login page or return an error response.
- Centralizes authentication logic
- Provides fast request filtering
- Protects protected routes efficiently
Database and Data Storage Security
Authentication protects the entry point, but your data storage layer must also be secure. Even if a user is logged in, they should only see the data they are permitted to access.
Implement row-level security or strict application-level filters to ensure one user cannot access another user's records. This is vital when offering website management services where data privacy is paramount.
- Use least privilege principles
- Encrypt sensitive database fields
- Sanitize all incoming user inputs
Common Pitfalls to Avoid
Many developers fall into traps that compromise their security posture. Avoid hardcoding secrets in your repository, which is a major security vulnerability that can lead to immediate compromise.
Another common issue is failing to revoke sessions upon user logout or password change. Always ensure your backend invalidates active tokens when a user performs a security-sensitive action.
- Storing secrets in plain text
- Insufficient session expiration times
- Ignoring security headers
- Over-exposing user profile data
Performance Considerations for Auth
Security checks can sometimes become a performance bottleneck if implemented incorrectly. Avoid making blocking network calls to an external database for every single request in your middleware.
Use short-lived, signed tokens that can be verified locally on the server. This provides the best balance between security and performance, which is essential for maintaining website performance optimization standards.
- Cache session verification locally
- Use cryptographically secure signing keys
- Minimize database hits on auth check
Scalability in Auth Systems
As your application grows, your authentication needs will change. A simple local database approach might work for an MVP, but you will eventually need a more robust identity provider.
Design your code to be modular so you can swap out your authentication provider later without rewriting your entire application. This flexibility is a hallmark of high-quality custom web development.
- Abstract auth logic into services
- Support multiple authentication providers
- Design for distributed session storage
Integration with Third-Party Providers
Integrating with providers like Google, GitHub, or Auth0 can simplify your development process significantly. These services handle the heavy lifting of password hashing, MFA, and account recovery.
However, you must still maintain strict control over how these providers interact with your application. Always validate the claims returned by the provider to ensure the user is who they claim to be.
- Verify issuer and audience claims
- Map user roles to internal permissions
- Maintain local user profiles securely
Conclusion
Implementing security in your application is a continuous process rather than a one-time setup. By following these guidelines for Next.js authentication, you can build applications that are both highly performant and secure.
Always stay updated with the latest security standards and library releases. A proactive approach to your auth stack is the best investment you can make for the long-term success of your software.


 In collaboration with